Key Takeaways
- Google researchers achieved a 40-fold reduction in errors, advancing the development of powerful quantum computers.
- Future quantum computers could potentially crack bitcoin’s cryptography, threatening wallets with exposed public keys.
- Researchers are exploring quantum-resistant protections, but upgrading the Bitcoin network presents significant technical and coordination challenges.
Google’s Latest Quantum Breakthrough
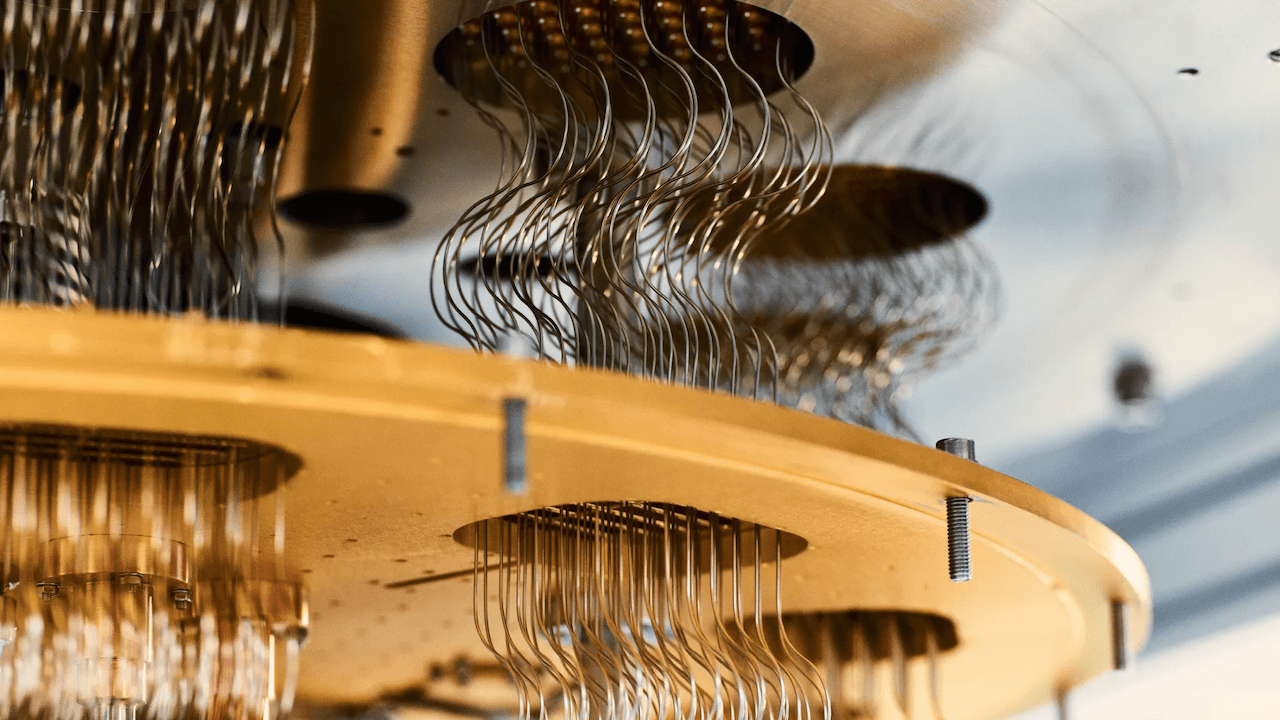
Google Quantum AI said Thursday that researchers successfully demonstrated a technique called “magic state cultivation” on the company’s Willow quantum processor, overcoming a longstanding obstacle to developing large-scale, error-corrected quantum computers.
The research, published in the scientific journal Science, achieved a 40-fold reduction in errors compared with quantum states that had not undergone the process. Researchers also produced so-called T-states with a record logical fidelity of 99.99%, demonstrating exceptionally high accuracy in a critical component of quantum computation.
Magic states are specialized quantum resources needed to perform certain operations essential for general-purpose quantum computing. Producing them reliably has been a major engineering challenge, with some estimates suggesting that as much as 95% of a quantum computer’s capacity could be devoted to their production.
Google’s technique addresses that bottleneck by introducing a noisy quantum state into a small region of a processor and using coordinated measurements to detect errors and eliminate flawed attempts.
The researchers also demonstrated a method for transferring purified quantum states between different error-correction architectures, an important capability for scaling quantum systems.
Although Google acknowledged that significant technical challenges remain, the company described the findings as a crucial step toward building useful, fault-tolerant quantum computers capable of solving problems beyond the reach of conventional machines.
Bitcoin’s Quantum Security Threat
The breakthrough adds to growing concerns about the eventual vulnerability of bitcoin’s cryptographic security to quantum computing, an expected milestone known as “Q-Day.”
In March, Google researchers published a separate analysis suggesting that breaking the elliptic-curve cryptography underlying bitcoin’s digital signatures could require fewer than 500,000 physical qubits, approximately 20 times fewer than some earlier estimates.
That research also outlined a theoretical scenario in which sufficiently advanced quantum computers could derive a bitcoin private key from an exposed public key in roughly nine minutes, potentially allowing attackers to intercept transactions before confirmation.
Researchers estimated that approximately 6.9 million BTC could face exposure through publicly revealed keys, including older wallet formats and addresses that have been reused.
However, no quantum computer currently exists that is capable of carrying out such attacks. Google’s latest magic state research does not demonstrate an ability to break Bitcoin’s cryptography, but it addresses one of the technical obstacles to developing machines that might eventually do so.
In September, Fidelity Digital Assets warned that sufficiently powerful quantum computers could eventually derive private keys from exposed Bitcoin public keys. The firm examined quantum-resistant signature systems, including a proposed approach called SHRINCS, while highlighting the complications posed by larger signatures that could reduce Bitcoin’s transaction throughput and increase fees.
The Challenge Ahead
Just this week, crypto exchange Coinbase published a detailed assessment outlining the challenges of transitioning Bitcoin to quantum-resistant cryptography.
The exchange, which says it safeguards approximately 15% of Bitcoin’s supply, emphasized that replacing existing signature algorithms would be only one part of the solution. Developers must also consider institutional custody systems, limited blockchain capacity, compatibility with existing wallets, and funds held in dormant addresses.
Coinbase pointed to proposals, including BIP-360, as potential foundations for introducing more adaptable cryptographic protections.
A particularly difficult question concerns bitcoin held in wallets whose owners have lost their private keys or are otherwise unable to migrate their funds to new security standards. Such holdings could remain exposed even after the network adopts quantum-resistant protections.
Google has separately targeted 2029 for migrating its own systems toward post-quantum cryptography, underscoring the broader industry’s preparations.
For Bitcoin, the challenge is not an immediate security failure, but the potentially lengthy process of coordinating upgrades across a decentralized network—before quantum computers become powerful enough to threaten its existing protections.